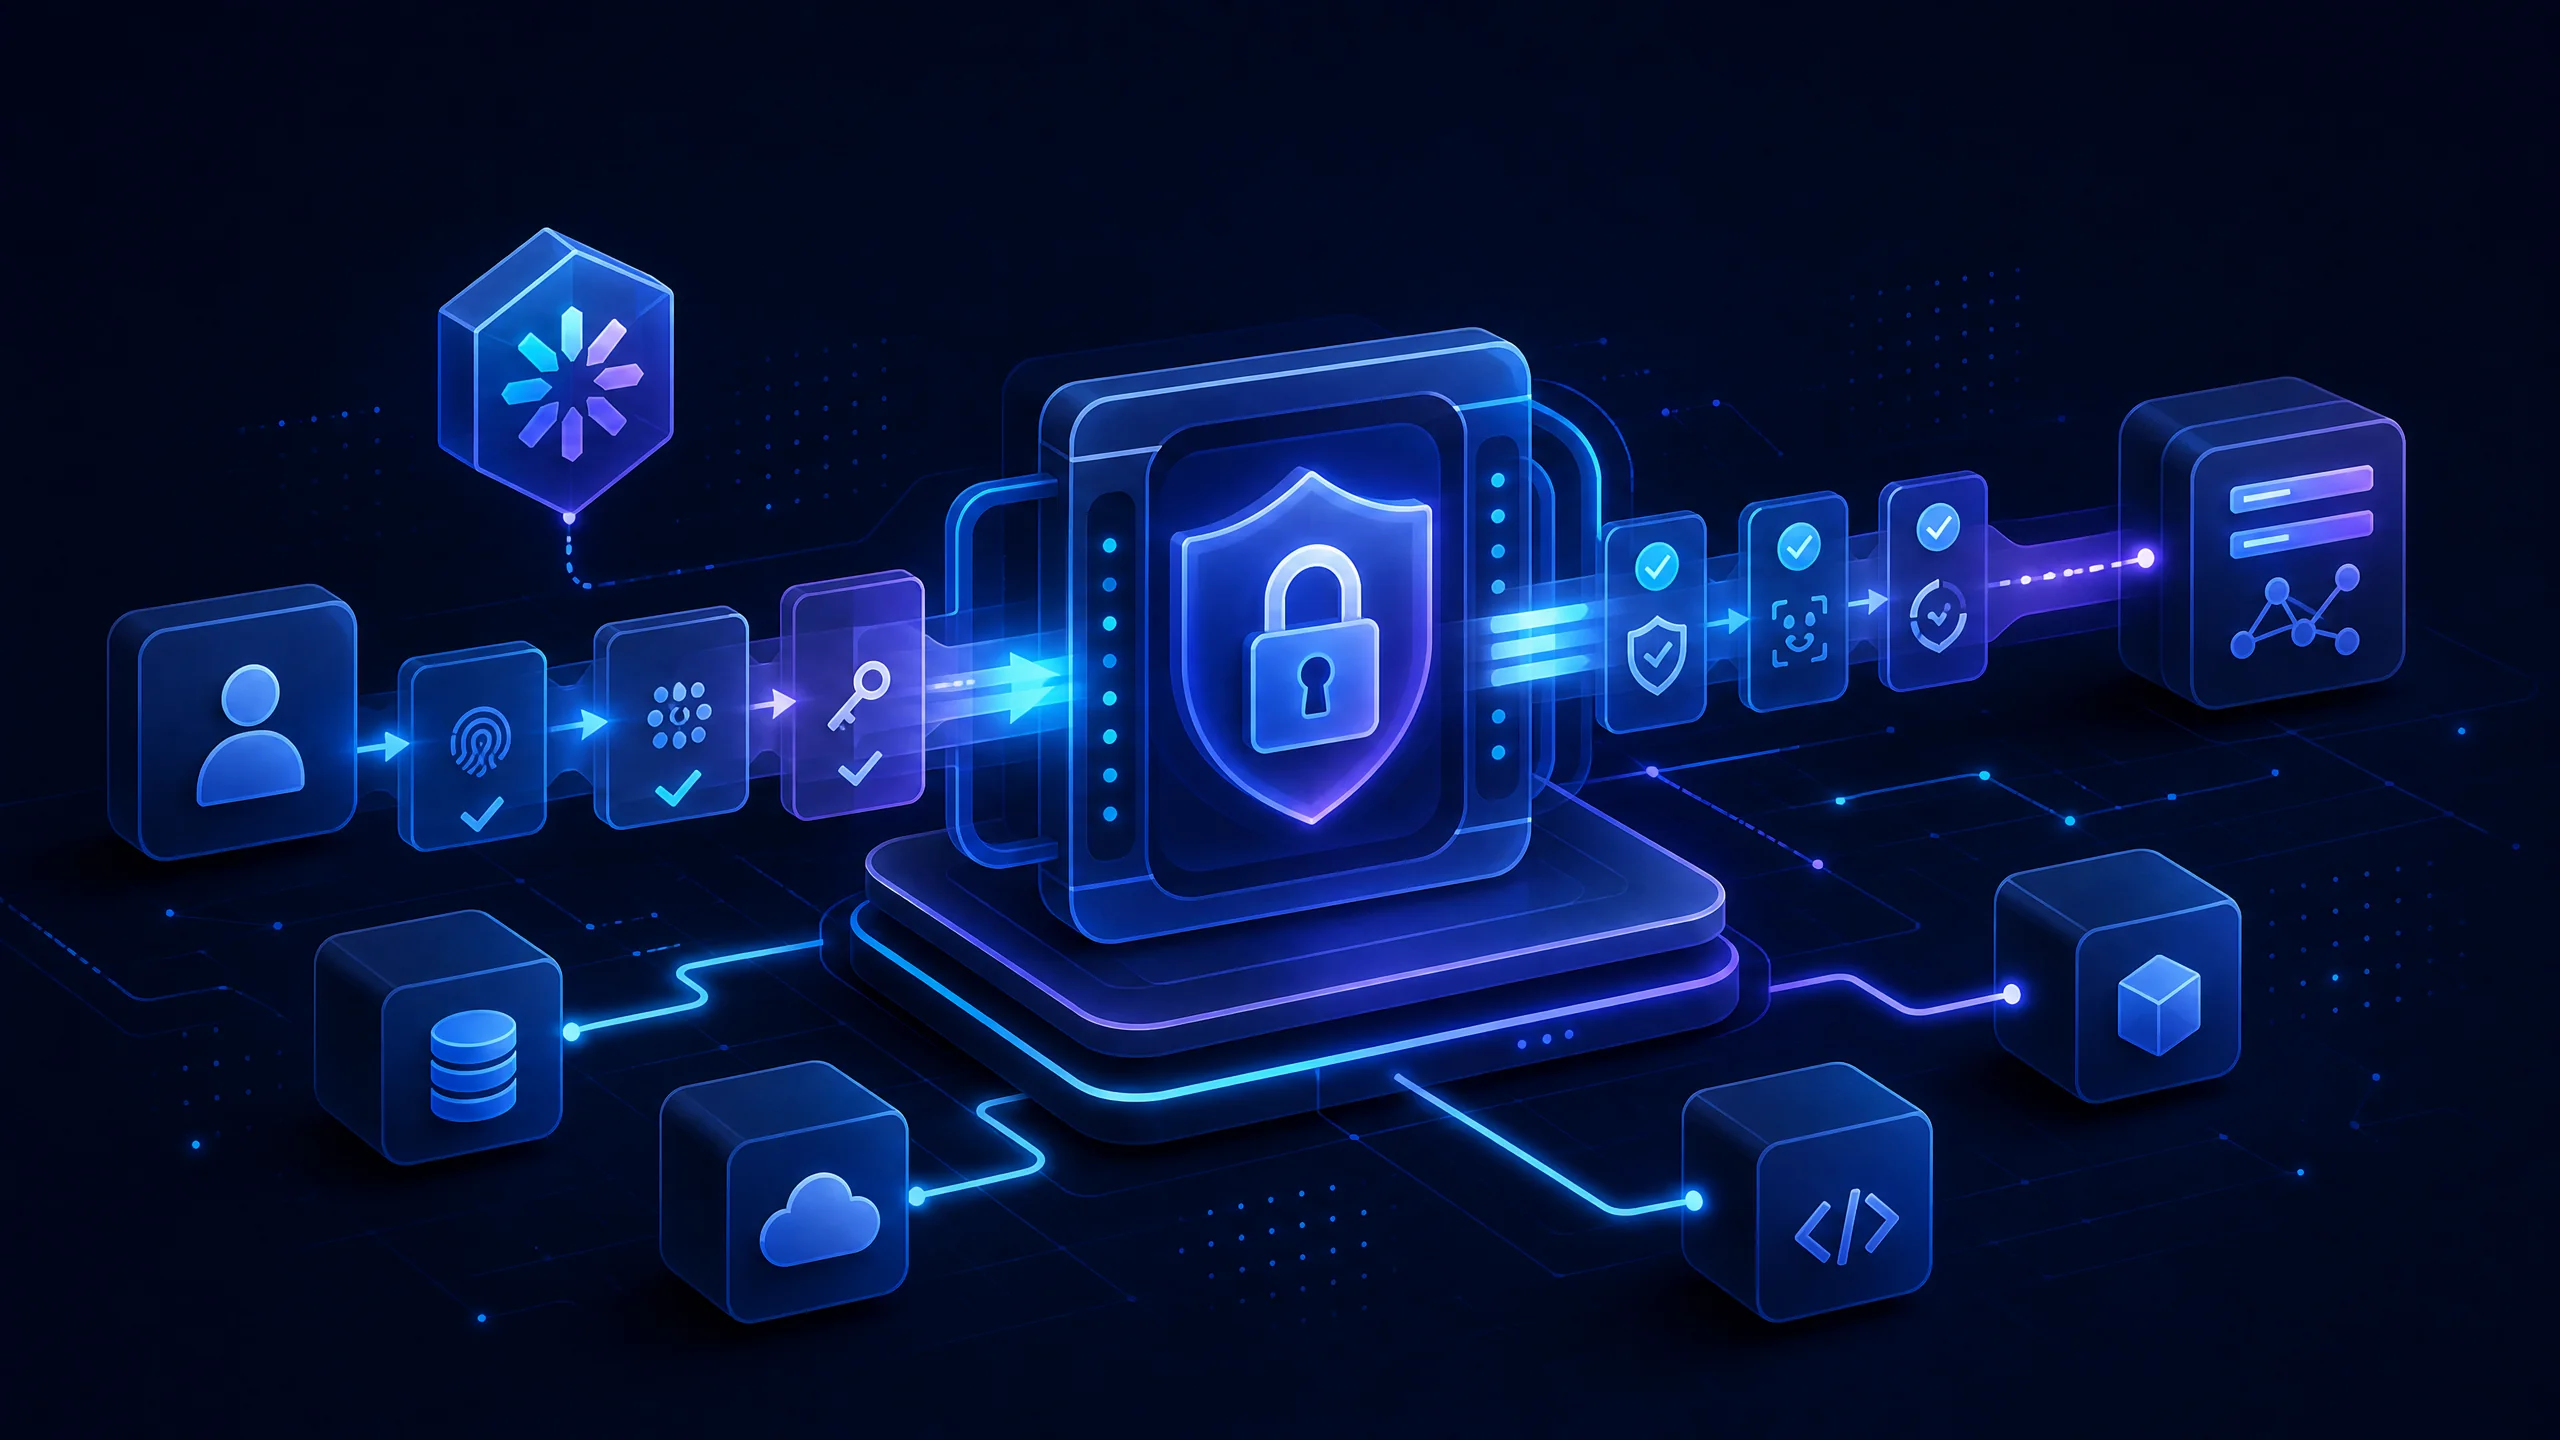
Authentication and authorization are different
Authentication answers who the user is. Authorization answers what that user may do. A valid token should never automatically grant access to every resource.
Keep access tokens short-lived
Short access-token lifetimes reduce the impact of theft. A refresh flow can issue a new access token after validating a refresh token, device state, and revocation policy.
Never store passwords directly
Use a slow, adaptive password hash such as Argon2 or bcrypt with an appropriate cost factor. Plaintext passwords and reversible encryption are not acceptable substitutes.
Check the resource owner
Role checks alone are not enough. An endpoint must also confirm that the requested record belongs to the current user or that the user has an explicit administrative capability.